
One counterpart for compliance work across Central Europe
One counterpart on your side, one method, one set of templates — and local delivery by whoever the local law allows.
Where
- Group presence
- Slovakia · Czechia · Poland · Hungary · Austria · Germany · Romania · Greece
Services
What we do
ISO/IEC 27001
Information security management: gap analysis, implementation, internal audits and preparation for certification by an accredited body.
ISO 22301
Business continuity: business impact analysis, continuity plans and exercises, preparation for certification.
ISO/IEC 20000-1
IT service management: processes, documentation and audit readiness.
TISAX / VDA ISA
Preparation for a TISAX assessment for automotive suppliers; the assessment itself is carried out by an ENX-accredited provider.
NIS2 — national transpositions
Scope assessment, registration, risk-management measures and self-assessment; the audit is performed by whoever the local law allows.
GDPR
Data protection officer as an external role, records of processing, impact assessments and training for authorised persons.
EU representative (Art. 27 GDPR)
For controllers and processors outside the EU: a contact point for data subjects and supervisory authorities, support with the required documentation, on the basis of a mandate agreement.
DORA
ICT risk-management framework, register of information and third-party contracts for financial entities.
AI Act
Classification of AI systems, obligations of providers and deployers, documentation. We are not a notified body.
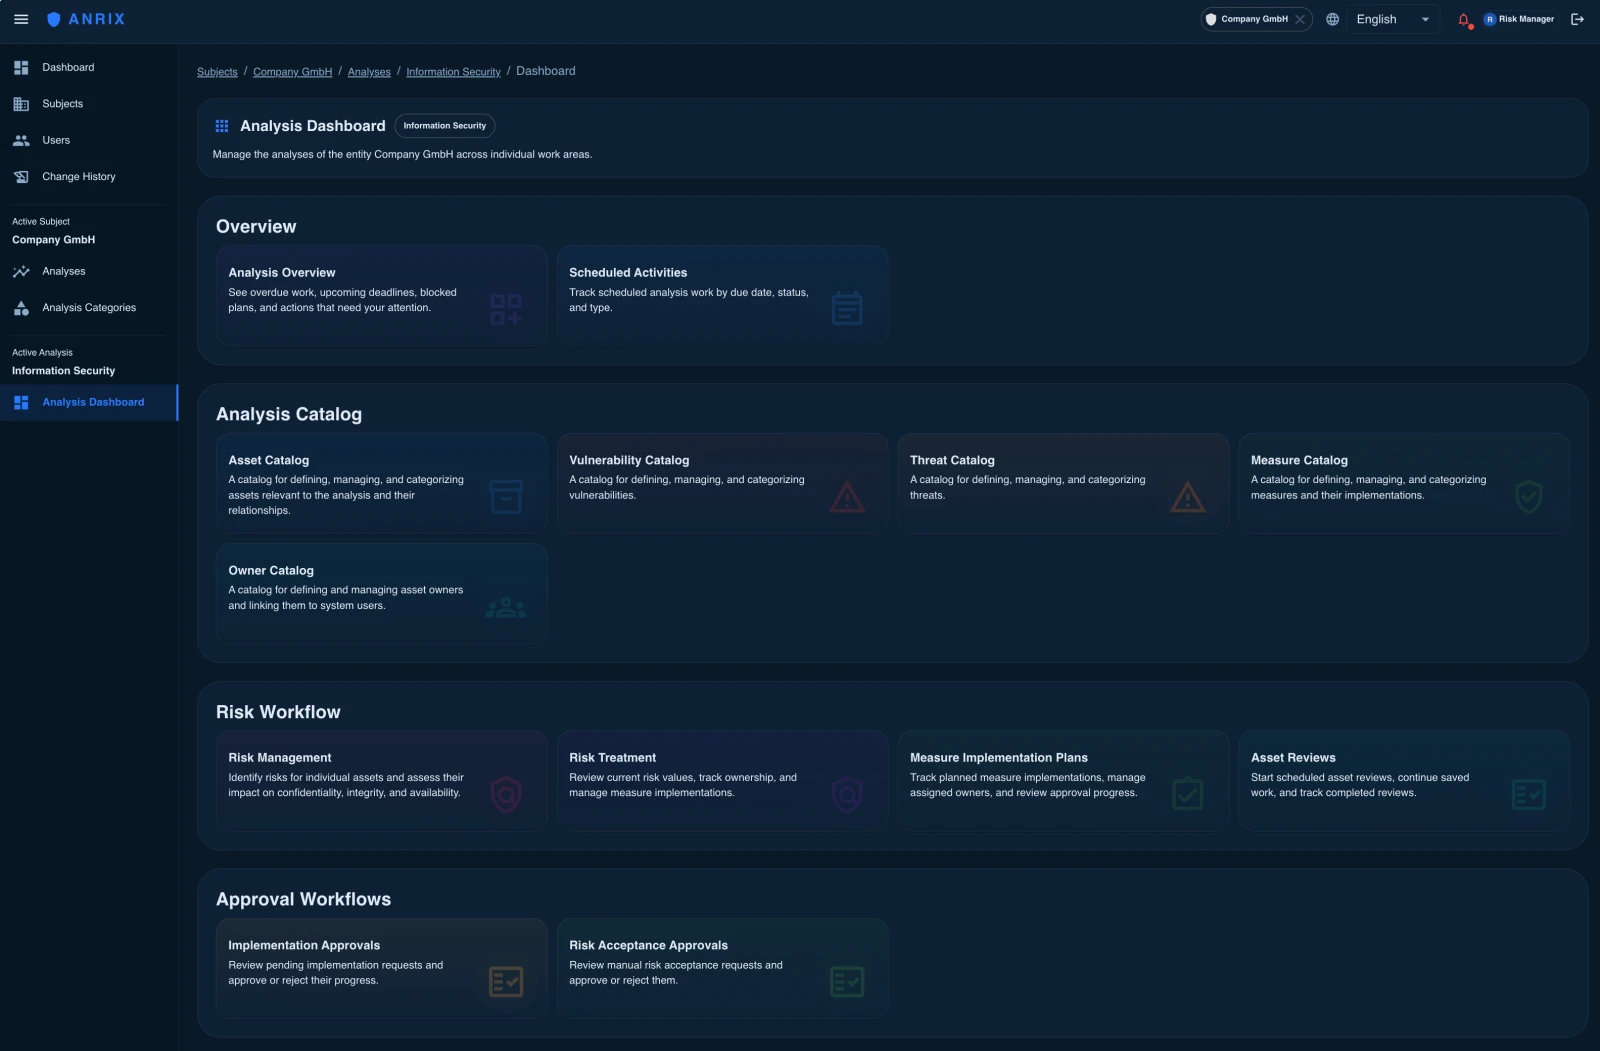
Risk analysis — as a service or as software
One risk analysis for three frameworks
ISO/IEC 27001, Article 32 GDPR and DORA all ask for the same thing: a register of assets, threats, risks and measures. It can be done once.
We do it with you
Method, templates and the register, worked through with your people.
Four questions tell you where your current analysis stands.
Why Anrix
On your server.
Anrix is installed in your own infrastructure; the data does not leave it.
Several entities, one scale.
Each company keeps its own register and approvals; head office sees all of them on the same scale.
One analysis, your languages.
The interface and the analysis run in the languages you work in; one analysis, no separate copies.
Built by auditors who use it.
The same system we use in our own audits and risk analyses.
NIS2 across eight countries
Whether an audit is required at all — and who is allowed to perform it — differs by country under NIS2.
| Country | Who may perform the audit | What that means in practice |
|---|---|---|
| Slovakia | certified cybersecurity auditor | certification and registration required |
| Czechia | a person trained in auditing, with at least three years' experience in performing cybersecurity or ISMS audits, who assesses independently and holds no other security role | open to foreign firms |
| Poland | an accredited conformity assessment body, or at least two auditors holding a recognised certificate; no Polish establishment required | open; first mandatory audits by April 2028 |
| Austria | an independent body (unabhängige Stelle) with an auditor admitted by the Austrian authority | EU establishment suffices; admissions not yet open |
Where to start
Three ways into the same portfolio
You are dealing with a regulation
You know which framework applies to you and you are looking for someone to take it on.
NIS2 · ISO/IEC 27001 · ISO 22301 · GDPR · DORA · TISAX · AI ActYou need a specific task done
You have a brief: an audit, a risk analysis, a gap assessment, documentation, or the data protection officer role as a continuing service.
Audit · risk analysis · records of processing · DPO · EU representative under Article 27You operate in several countries
You need the same method to hold across the group — and to know who may perform the audit in each country.
Eight countries · one method · one set of templatesWhy one counterpart
How one method survives eight legal systems
If your group operates in several European countries, you already know the shape of the problem. Eight suppliers, eight methodologies, eight report formats — and nobody who can tell you whether it adds up. Each of them is right about their own country. None of them is responsible for the whole.
We work the other way round: one counterpart on your side, one method, one set of templates — and local delivery by whoever the local law allows.
Scope definition, risk methodology, evidence structure, self-assessment and management review can be identical in every country. The audit is then a local act performed by whoever the local law allows — and because the evidence underneath it was built the same way everywhere, that local act is short.
The part that most groups underestimate is self-assessment. Several countries require it annually alongside or instead of the audit, no certificate comes out of it, and it is therefore the first thing that gets neglected. It is also the part that a group can genuinely run centrally: one method, one evidence format, one calendar.
Boundaries
Where our work ends
No penetration testing
We do not perform penetration tests or threat-led penetration testing. We prepare the organisation, coordinate the process and assess the result; the test itself is carried out by an independent provider.
Nobody audits their own work
Where we hold the security manager role at a client, we do not audit that client.
We do not issue certificates
Certificates against ISO/IEC 27001 and ISO 22301 are issued by an accredited certification body, not by an advisor. TISAX assessments may only be performed by an ENX-accredited provider — we prepare, we do not assess.
Proof instead of names
What can be verified
- 17 260
- clients of the group
- 8
- European countries the group operates in
- 2010
- the year the IOSEC group was founded
- 8
- frameworks and standards we work in
We publish no client names or logos — that is a decision, not a gap.
Knowledge
What we have written about it
The AI Act: what applies today and what was postponed to December 2027
If you marked the August date as the day the AI Act would land on you, you were half right. The obligations for high-risk…
Why an IT service provider is a processor
An external technician connects to your server, opens the database and fixes a bug. It takes ten minutes and nobody treats it as…
How to correctly mark a monitored area
EDPB Guidelines 3/2019 say what has to be on the sign at the entrance to a monitored area and what it is enough to make…
Tell us what you are dealing with.
Thirty minutes with a consultant who knows your industry. The output is a one-page summary with a recommended approach and an indicative scope — we send it to you even if we do not reach an agreement.