
Anrix: risk management system
One risk analysis for the Slovak Cybersecurity Act, ISO/IEC 27001, the GDPR and DORA — in your infrastructure, for all your entities.
Who it is for
- Groups with several companies that want one risk register and one head-office view instead of spreadsheets from each company.
- Public authorities with organisations under their remit — one installation, each organisation with its own register and owners.
- Financial entities and their groups that need ICT risk management under DORA in one place for every company in the group — see Digital operational resilience (DORA).
- Organisations that want to keep the analysis in-house — the system runs on your server and the data never leave your environment.
What Anrix does
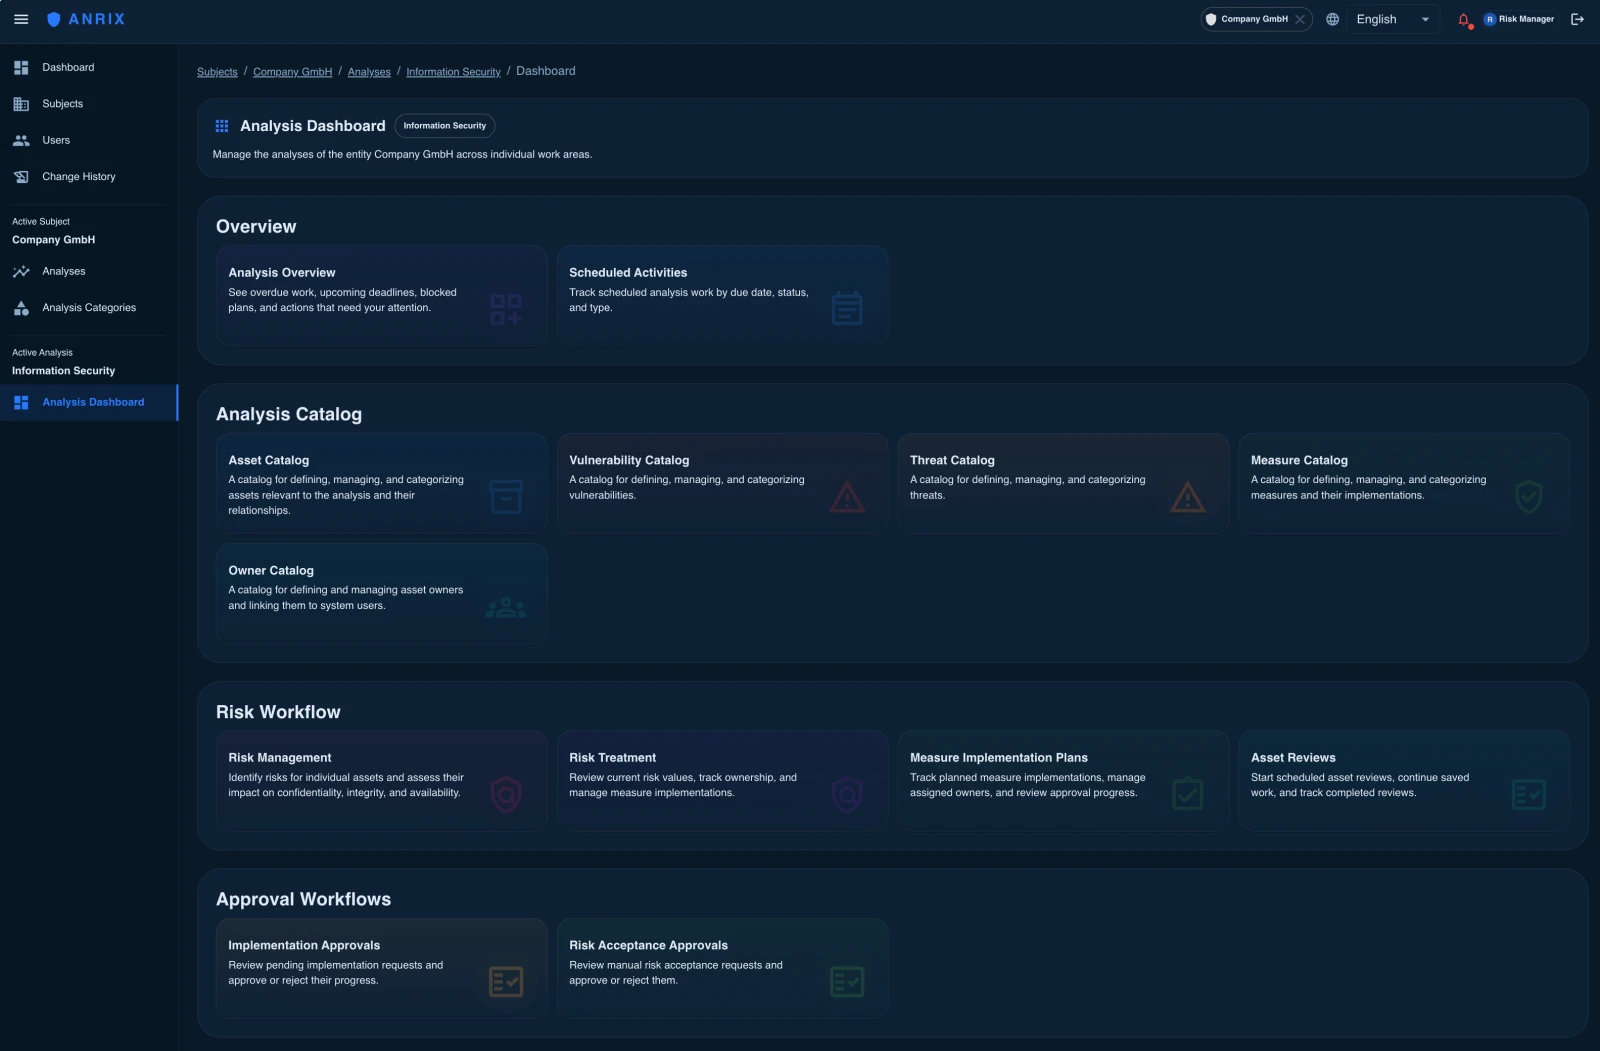
- a register of assets, threats, vulnerabilities and risks with asset – risk – measure links; every asset has an owner,
- assessment on a configurable scale (likelihood × impact) with an acceptability threshold according to your methodology,
- a decision on accepting residual risk with formal approval — who and when,
- an action plan with deadlines, owners and status; linked to Decree No. 227/2025 Coll. and Annex A of ISO/IEC 27001,
- a change history for every record — an immutable trail for audit,
- periodic review of the analysis with the date and result recorded.
Several entities, one view
Each company or organisation has its own register, owners and approvals, with data kept separate. Head office sees them all on the same scale — where risks repeat and where measures are late.
One analysis, several languages
Interface in Slovak, Czech and English. The content of the analysis is available in every language without separate copies — the local administrator works in their language, head office reads in its own.
Operation
Anrix runs in your infrastructure (Linux, container deployment), accessed through a browser with nothing installed on end devices. We provide updates, fixes and support under an agreed service level; the data stay with you.
Methodology and outputs
The analysis follows the methodology of the Slovak National Security Authority and supports compliance with Act No. 366/2024 Coll., Decree No. 227/2025 Coll., ISO/IEC 27001 and Article 32 of the GDPR — with one analysis, not three. For financial entities under Regulation (EU) 2022/2554 (DORA), the analysis serves as the basis of the ICT risk management framework (Article 6) and of the identification and classification of assets and risks (Article 8); mapping of measures to DORA requirements is added on request, like other catalogues. The threat catalogue is based on ISO/IEC 27005. Outputs: risk list with ratings, proposed measures, residual-risk acceptance proposal, risk report for management and the auditor.
Licence
Annual licence, multi-year on request; includes updates and support. Price depends on the number of entities in the installation — on request.
For public contracting authorities
We have a functional description of the subject of procurement ready, without a manufacturer's name and with CPV codes — on request.
What Anrix is not
- It does not decide for you — risk acceptance is approved by an authorised person; the system records it.
- An analysis we prepared with you in Anrix is not audited by the same team.
Demo and trial access
We will show you Anrix remotely on your own examples, or set up trial access for 14 days from first login.
Tell us how many entities you want to manage — we will arrange a demo or trial access.
Tell us what you are dealing with.
Thirty minutes with a consultant who knows your industry. The output is a one-page summary with a recommended approach and an indicative scope — we send it to you even if we do not reach an agreement.